Security
Controls for the inbox your team depends on.
Protect customer and client inquiries with two-factor authentication (2FA), role-based security, encrypted sensitive data, audit logs and human guardrails for AI. These shared controls support every industry Intaque serves.
From home services and legal teams to healthcare, property management and financial services, your team uses the same core security controls. Explore industry applications.
2FA (two-factor authentication)
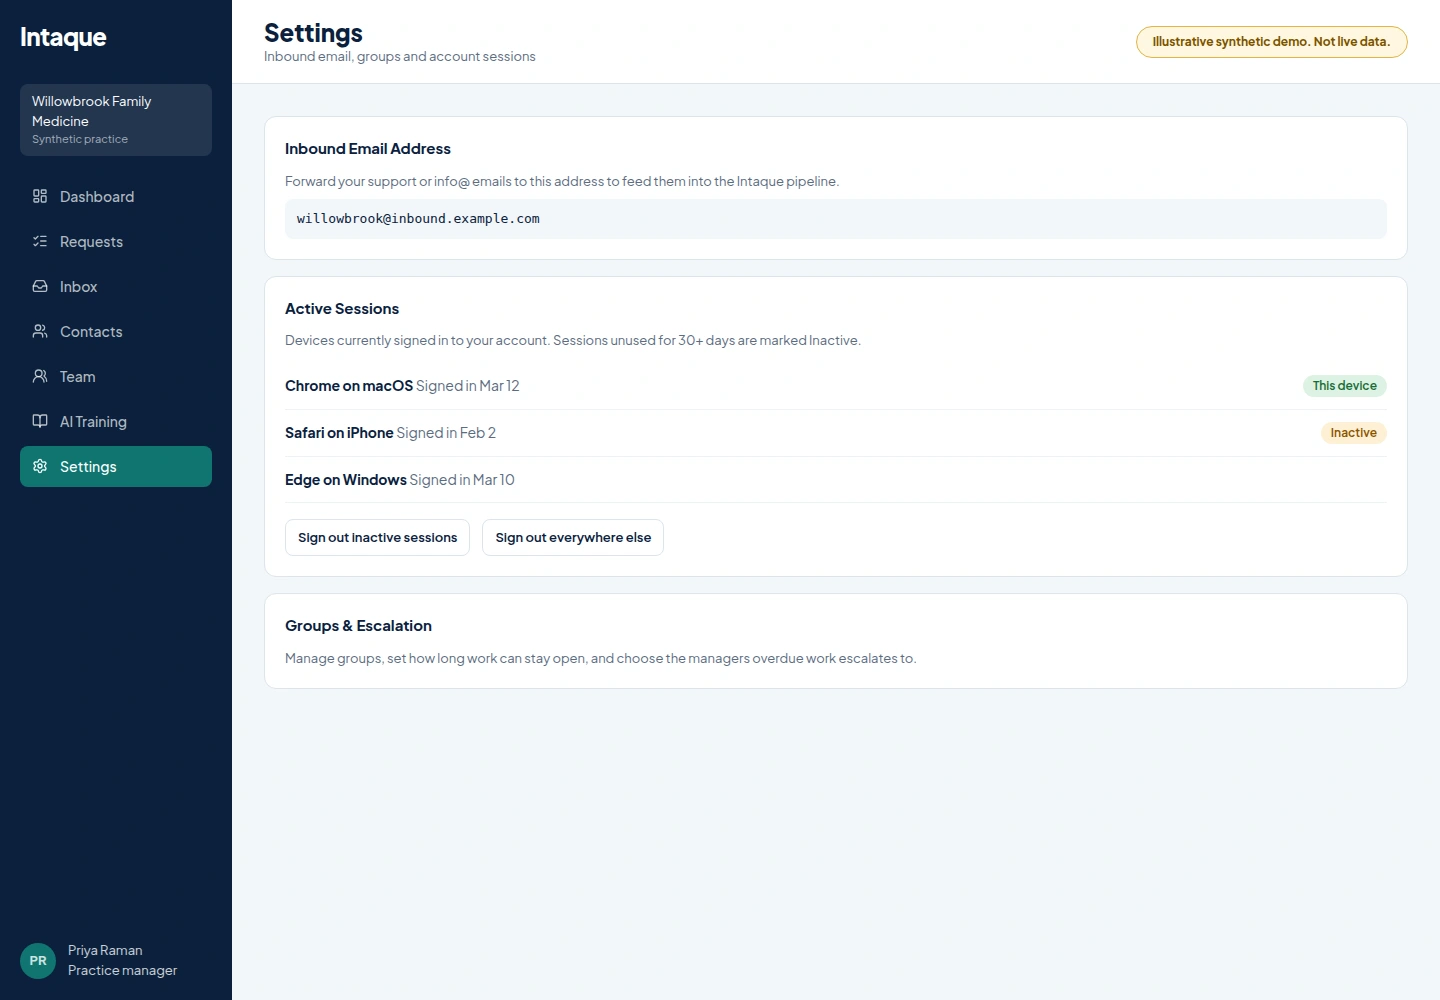
Sign-in requires your password and a one-time verification code sent to your email, with session controls to review and revoke access.
Role-based security
Assign different roles to users within your organization. Each user's role controls what they can access and do in the application.
Encrypted sensitive fields
Sensitive data stored in Intaque is encrypted in the database and at rest. Traffic uses HTTPS for secure communications to and from the system.
Audit logs
All actions by users, AI and developers in the system are logged for audit and security purposes.
AI security and human guardrails
Human guardrails require approval for all AI actions. Intaque.com uses the OpenAI API with a signed Business Associate Agreement (BAA) for additional security and safety when handling PHI.
Bounded MCP scopes
Per-user, admin-enabled, audit-logged. Drafts are copy-only.
Healthcare: PHI, HIPAA and BAA requirements
Intaque.com is HIPAA compliant. The following requirements apply to medical practices handling protected health information through Intaque.
Before handling protected health information (PHI) through Intaque, medical practices must sign a Business Associate Agreement (BAA) with Inspection-Ready Institute, Inc., DBA Intaque.com, for the required legal protections and HIPAA/HHS compliance.
Intaque.com encourages medical practices handling PHI through email or their website to review this agreement with their legal counsel before signing.
Contact [email protected] to request a copy of our Business Associate Agreement. Until a BAA is signed by both parties, keep PHI out of Intaque.
Request a copy of our BAAOperational contact management across industries means names, emails and the question being asked, so staff know who owns the reply. The platform's shared security controls are not limited to healthcare.
Handling PHI through email or your website requires a signed BAA with Inspection-Ready Institute, Inc., DBA Intaque.com. Review the agreement with your legal counsel before signing. Intaque is not an EHR, emergency triage or clinical decision software.
Common questions
Frequently asked questions
Do these security controls apply outside healthcare?
Yes. Intaque supports teams across industries, including home services, legal, healthcare, property management and financial services. Two-factor authentication (2FA), role-based security, encrypted sensitive data, audit logs and human guardrails for AI apply across the platform.
How is access to our organization's inquiries controlled?
Administrators can assign different roles to users within their organization. Role-based security controls what each user can access and do. Administrators can also review and revoke sessions, and MCP access is enabled per user with bounded scopes and audit logging.
How does two-factor authentication (2FA) work?
Sign-in requires your password plus a one-time verification code sent to your email. This second verification step uses email, rather than an authenticator app or SMS. Session controls also let you review and revoke access.
Is Intaque HIPAA compliant?
Intaque.com is HIPAA compliant. Before handling protected health information (PHI) through Intaque, medical practices must sign a Business Associate Agreement (BAA) with Inspection-Ready Institute, Inc., DBA Intaque.com, for the required legal protections and HIPAA/HHS compliance. Intaque.com encourages medical practices handling PHI through email or their website to review this agreement with their legal counsel before signing. Contact [email protected] to request a copy of our Business Associate Agreement.
How do I obtain a BAA?
Before handling protected health information (PHI) through Intaque, medical practices must sign a Business Associate Agreement (BAA) with Inspection-Ready Institute, Inc., DBA Intaque.com, for the required legal protections and HIPAA/HHS compliance. Intaque.com encourages medical practices handling PHI through email or their website to review this agreement with their legal counsel before signing. Contact [email protected] to request a copy of our Business Associate Agreement. A BAA must be signed by both parties before PHI is handled through Intaque.
Does Intaque hold PHI?
Intaque manages operational inquiries, which may contain PHI when received through email or a website. Website form capture redacts sensitive fields. Before handling protected health information (PHI) through Intaque, medical practices must sign a Business Associate Agreement (BAA) with Inspection-Ready Institute, Inc., DBA Intaque.com, for the required legal protections and HIPAA/HHS compliance. Intaque.com encourages medical practices handling PHI through email or their website to review this agreement with their legal counsel before signing. Contact [email protected] to request a copy of our Business Associate Agreement.
Give every inquiry an owner by Monday.
Connect a form, set up your office groups and let your team see what needs them next.